 Risk Management Program
A consultant-led cyber risk program: 19 assessment activities, run on a recurring cadence by one team, quantified in financial terms, with the tooling included.
Start at Core and grow into Plus and Enterprise as your organization’s needs and capabilities mature. The methodology, scoring and reporting stay identical across tiers, so you maintain risk trending context.
Risk Management Program activities span the digital, cyber and physical footprint. Select any activity to read what it covers.
| Program activity | CORE | PLUS | ENTERPRISE | Activity frequency |
|---|
Findings are contextualized and prioritized so you can make risk-informed decisions when they matter.
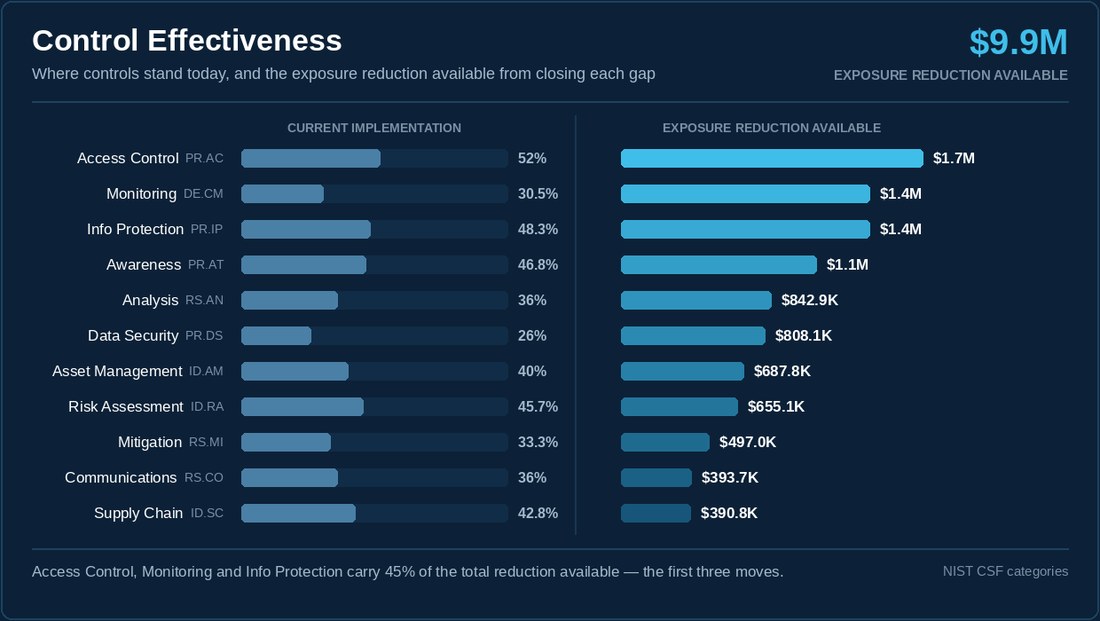
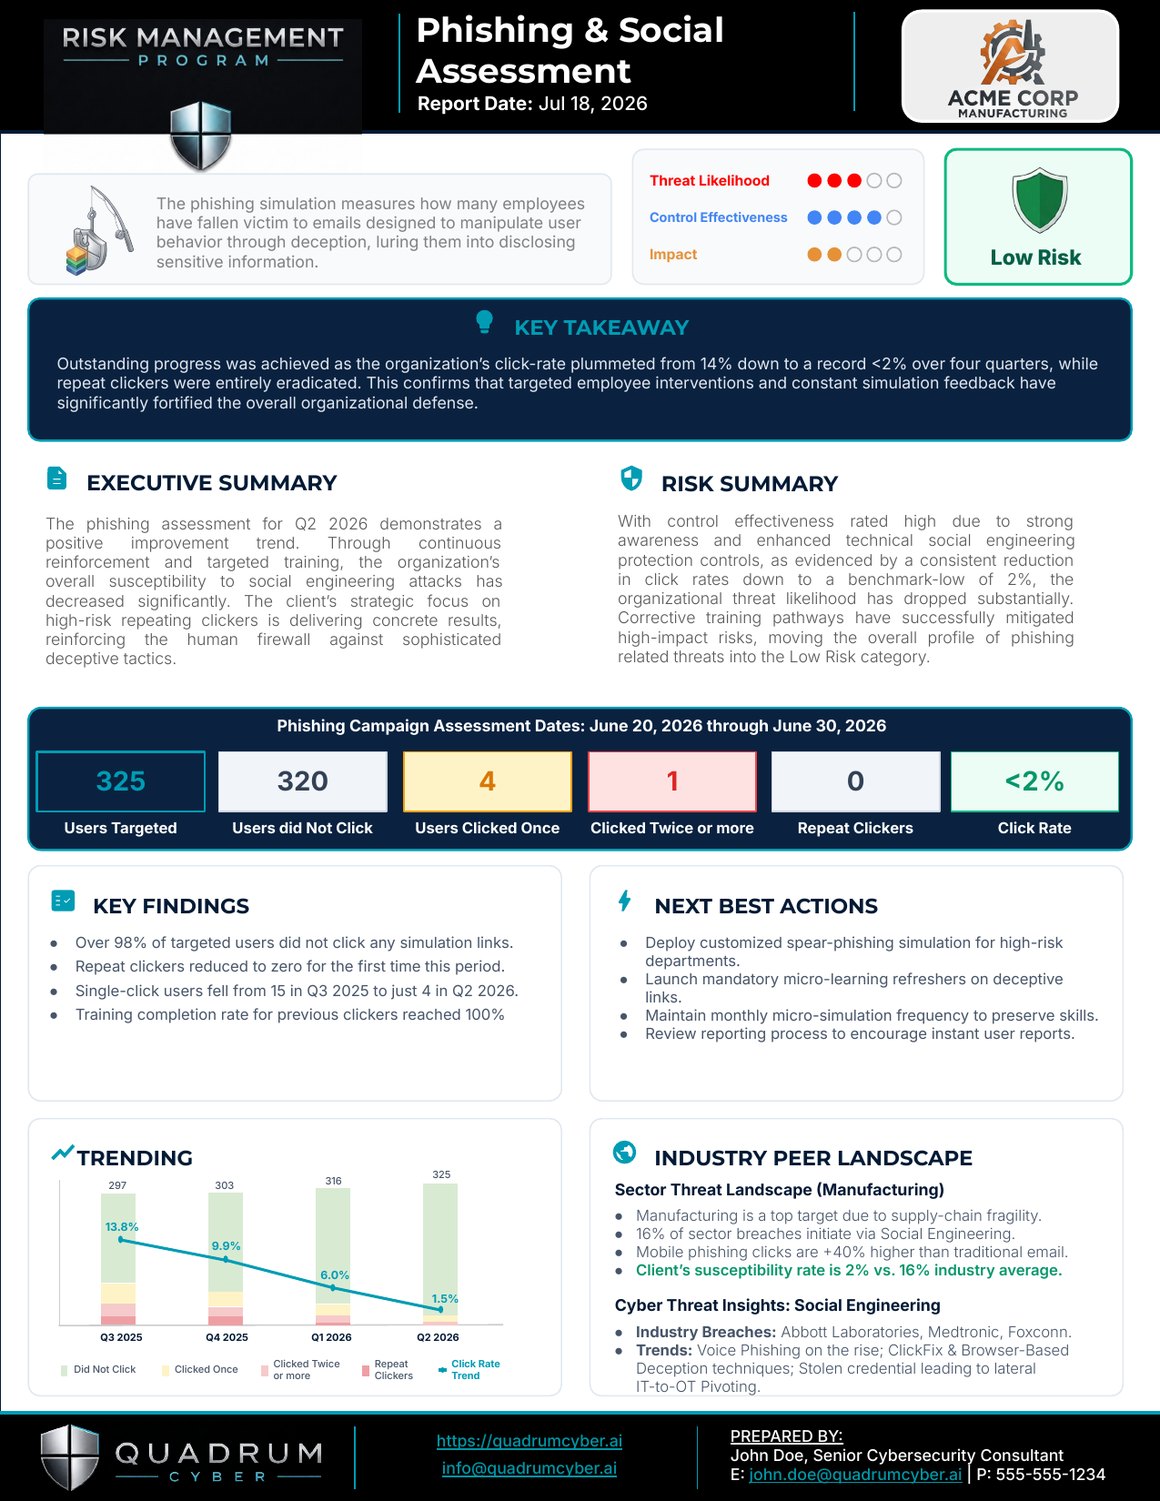
What the program delivers on every cycle.
Issued for each assessment activity. Every finding carries its severity, a summary of the risk, the potential business impact, and the specific remediation steps to close it.
Front of every Assessment Report: the result analysed on a single page and set against industry peers, so the conclusion survives the walk to the boardroom.
Everything performed that quarter in one place — risk metrics with KPIs and KRIs, quarter-over-quarter trends, and a prioritized list of risk-reduction recommendations.
Reporting is never re-run or re-scored for a given audience — it is the same measurement, contextualized for the decision each reader actually makes.
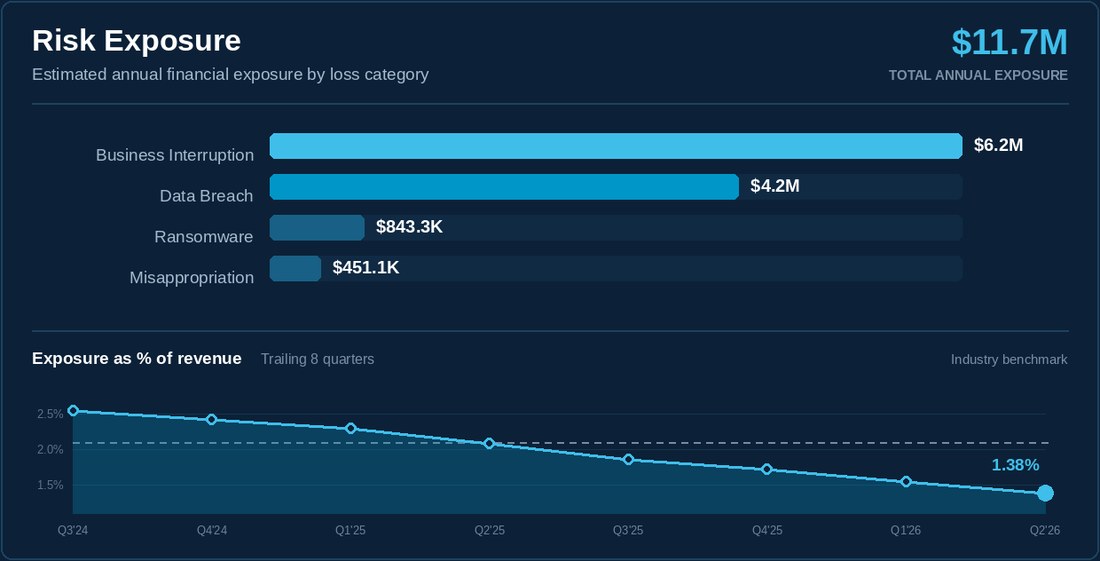
Exposure in dollars, the trend line, and whether oversight duties are being met.
What the last dollar bought, what the next one should, and the operational risk behind it.
Control effectiveness across the domain areas, ranked by exposure removed per dollar.
The findings themselves — severity, evidence, affected assets and the fix.
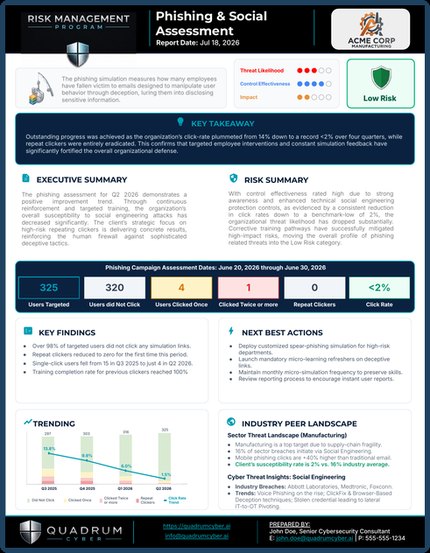
Executive summary · risk rating · control effectiveness · key findings · next best actions · industry peer landscape · quarter-over-quarter trending — all from the same measurement the practitioner is working from, written for the person who has to make the call.
Select the report to view it full size.
Risk quantification grounded in nearly two decades of actuarial data — built in and enabled from the Core tier, not sold as a premium module.
Consistent reporting, scoring and trending across every activity. Nobody is left stitching five vendors' PDFs into a board narrative.
Seasoned practitioners run the assessments and interpret them. The platform carries the evidence; the advisor carries the argument.
Ransomware susceptibility and privileged account controls are program activities — because that is where the breaches are.
QuadRMP Certification is awarded exclusively to Risk Management Program clients who have met and maintained every requirement of the program, and who have been brought before a Certification Board of globally recognized cybersecurity experts and leaders. It is not a questionnaire, a self-attestation or a logo that comes with the contract.
Full delivery of the activities in your tier, with findings remediated to the agreed thresholds — not merely reported and carried forward.
Certification reads a trend line, not a moment. Performance has to be sustained across consecutive delivery cycles, and it is re-tested every year.
Posture and evidence are presented to a Certification Board of globally recognized cybersecurity experts and leaders, who decide. Quadrum does not award it alone.
Certification is held for as long as program requirements continue to be met, and is withdrawn if they are not.
We will walk your environment through the program model and show you what the first cycle would measure.